Sign Protocol: Attestation Architecture
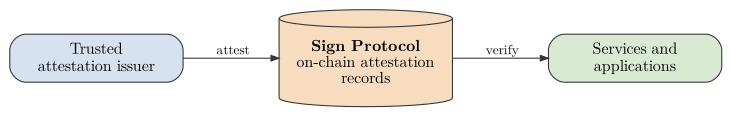
Sign Protocol is an on-chain attestation framework for creating, verifying, and revoking signed attestations (Figure 4).
How Attestations Work
Sign Protocol has the following capabilities:
-
Attestation Creation: Authorized entities can issue signed attestations about people, organizations, assets, and records.
-
Verification: Anyone authorized can check an attestation’s signature and issuer, and whether it has been revoked or has expired.
-
Revocation Infrastructure: Attestations can be revoked when necessary.
-
Expiration Management: Time-bound attestations expire automatically.
-
Selective Disclosure: A holder can disclose some fields of an attestation without revealing the rest.
Government applications that need trusted verification of facts, credentials, or claims can build on Sign Protocol, on public blockchains and on permissioned ledgers.
Interoperability Across Ledgers
Sign Protocol attestations interoperate across both ledger infrastructures in the SIGN Stack:
-
Unified Identity Framework: The same identity attestation can support a bank’s onboarding to the CBDC and an eligibility check by a smart contract on the public path.
-
Privacy-Preserving Verification: Zero-knowledge proofs enable identity verification on public chains without exposing sensitive personal data held by identity issuers and banks.
-
Compliance Bridging: Identity attestations let anti-money laundering and counter-terrorist financing (AML/CFT) checks follow the same rules in both blockchain environments.
-
Anchor for the DataHub: The DataHub is designed to record its anchors as Sign Protocol attestations, one per record or one per batch, so a credential, a license, and a data exchange are verified the same way on either ledger.
Privacy Preservation
Sign Protocol supports zero-knowledge proofs (ZKPs) to balance verification needs with privacy protection:
-
Selective Disclosure: Users can prove specific attributes (age, nationality) without revealing full data.
-
Unlinkability: With BBS-based or zero-knowledge formats, presentations cannot be linked across contexts.
These capabilities are designed to support compliance with data protection law while still allowing the verification each service needs.